API Scanning
Import an OpenAPI definition file and run a vulnerability scan of your API using the ZAP scanner.
Steps to set up an API scan
1. Create a new target
In your HostedScan account, navigate to the Targets screen and click the "Add Targets" button.
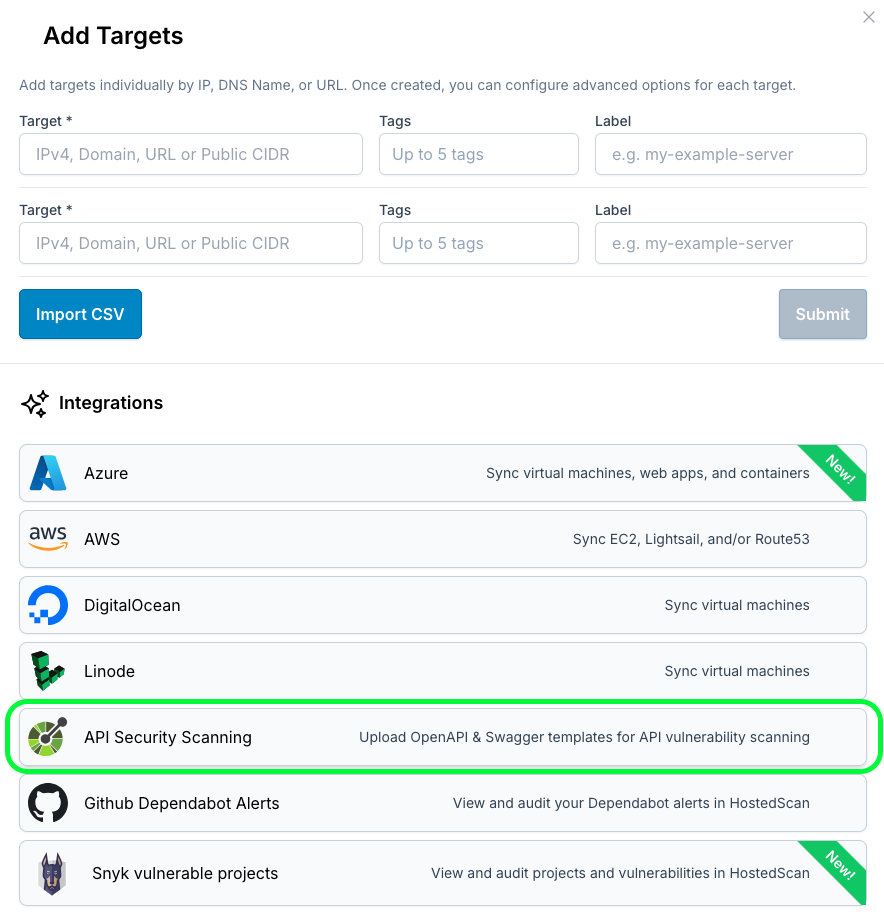
2. Select the API Security Scanning option
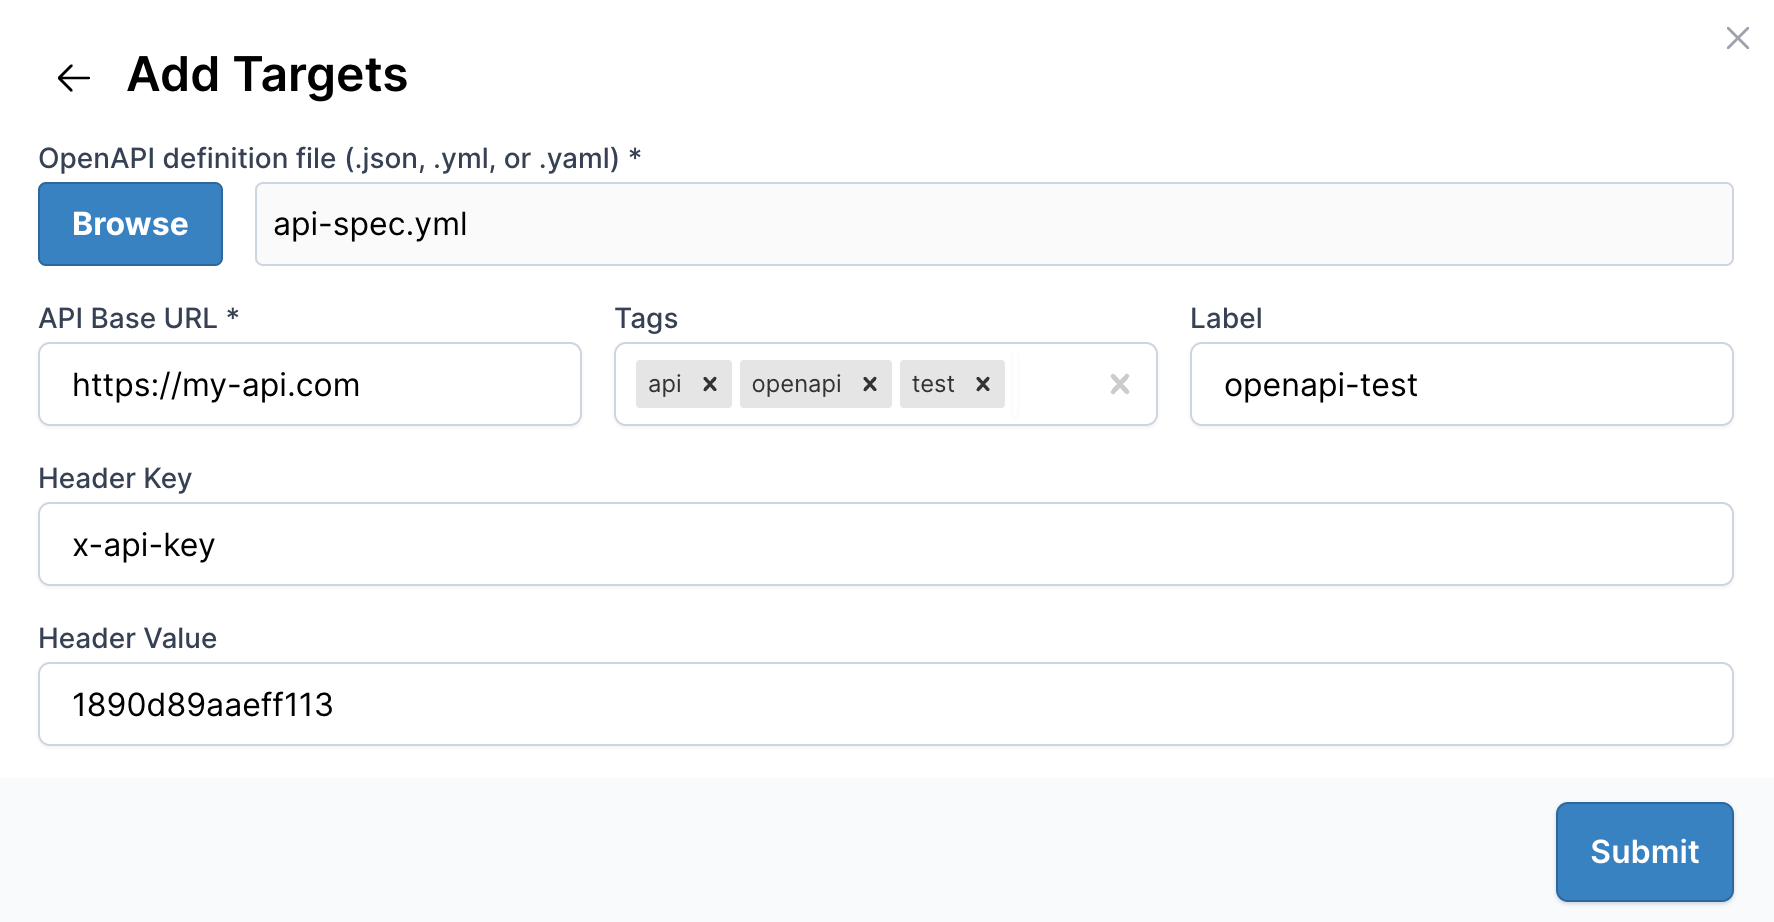
3. Upload your OpenAPI definition file
4. Run a scan!
- Click the "New Scan" button
- Select the OWASP ZAP Active Web Application Scan
- Select your target
- Continue through the scan options and click "Run Scan"